Categories
Directory Service Kerberos Linux Samba

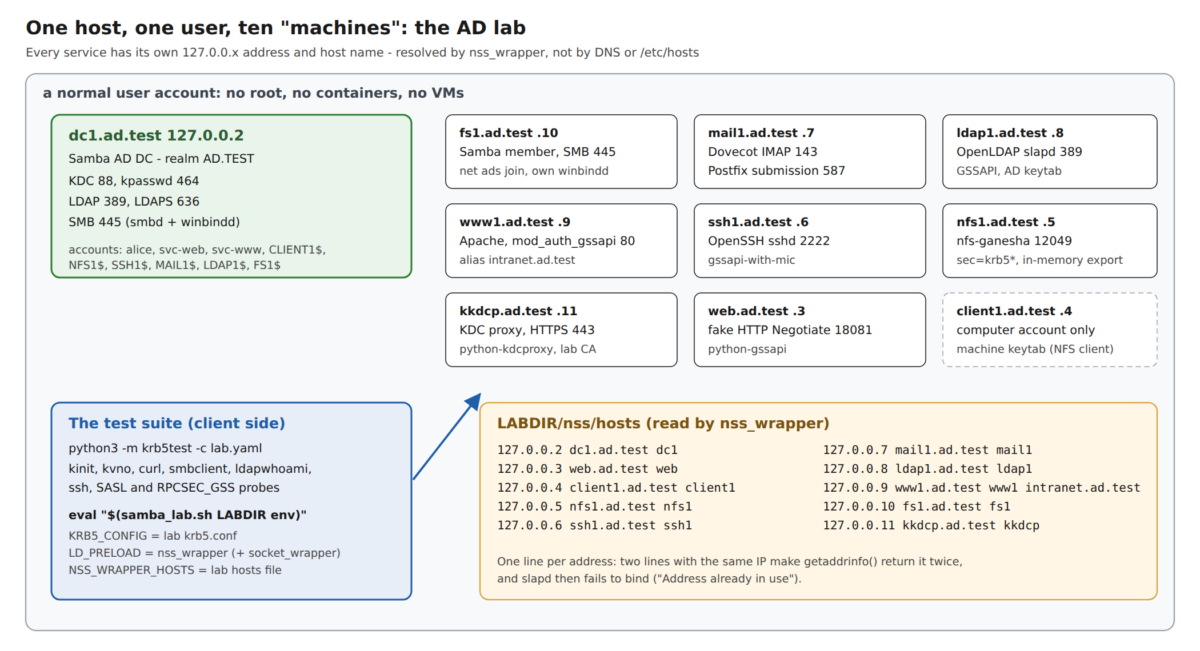
A complete Active Directory lab without root: Samba, NFS, mail, LDAP and Apache with cwrap

A Samba AD domain with a member file server, NFS, IMAP/SMTP, OpenLDAP, Apache and a KDC proxy, set up by one script, as a normal user, without containers or VMs, if needed even without real network ports. How cwrap’s uid_wrapper, nss_wrapper and socket_wrapper make that possible, and the traps each daemon had in store.
Categories
Directory Service Kerberos LDAP

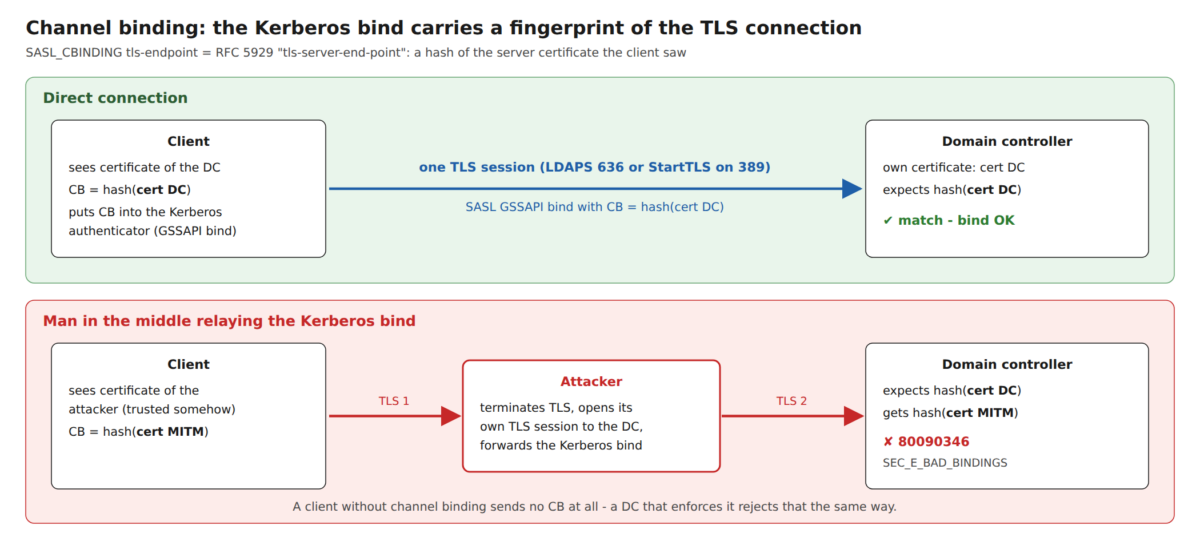
LDAP over TLS against Active Directory: channel binding, maxssf=0 and error 80090346

GSSAPI binds over LDAPS or StartTLS fail against hardened domain controllers with 80090346 or ‘Sign or Seal are not allowed if TLS is used’. Reproduced against a Samba AD DC with real output: what channel binding and the SASL security layer have to do with it, the two client settings that fix it, the matching server setting, and two traps when OpenLDAP itself accepts AD tickets.

Categories
Kerberos Samba

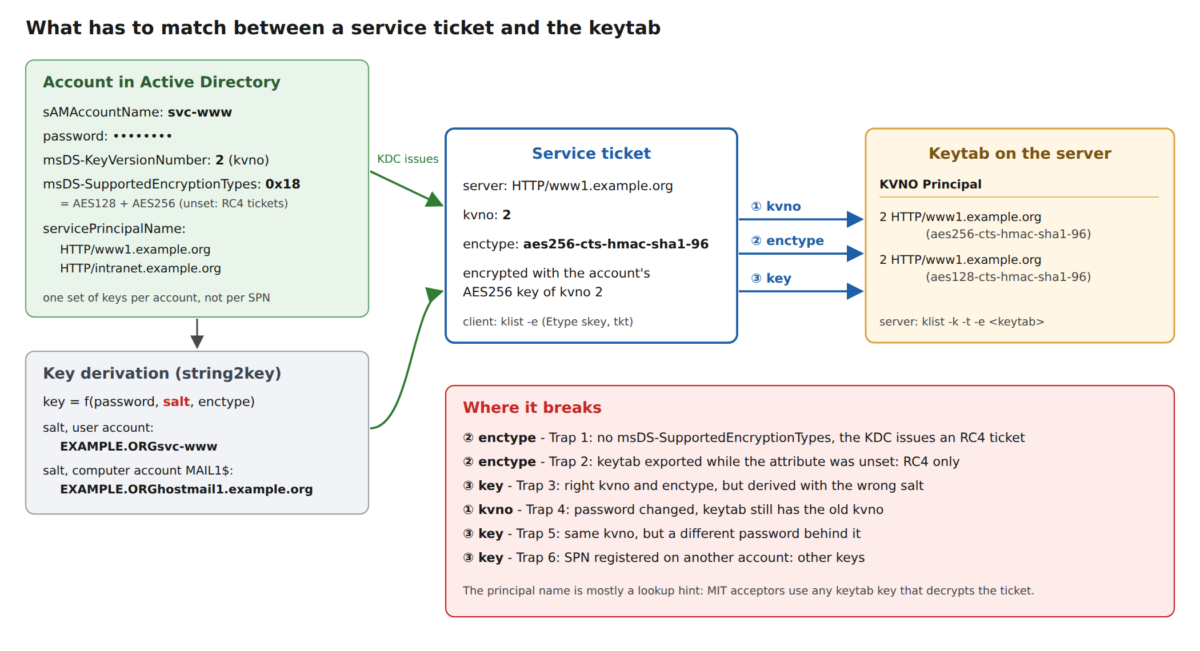
Your keytab is lying to you: kvno, enctypes and salts in Active Directory

kinit works, the service ticket looks fine, and the server still says 535 5.7.8 or HTTP 401. Almost always the server’s keytab does not hold the key the KDC used. Six traps in Active Directory and Samba, each reproduced in a lab with real output: RC4 tickets, RC4-only exports, AES salts, kvno drift, same kvno with a different key, and SPNs on the wrong account. Plus a flowchart to find the cause.

Categories
Kerberos Proxy

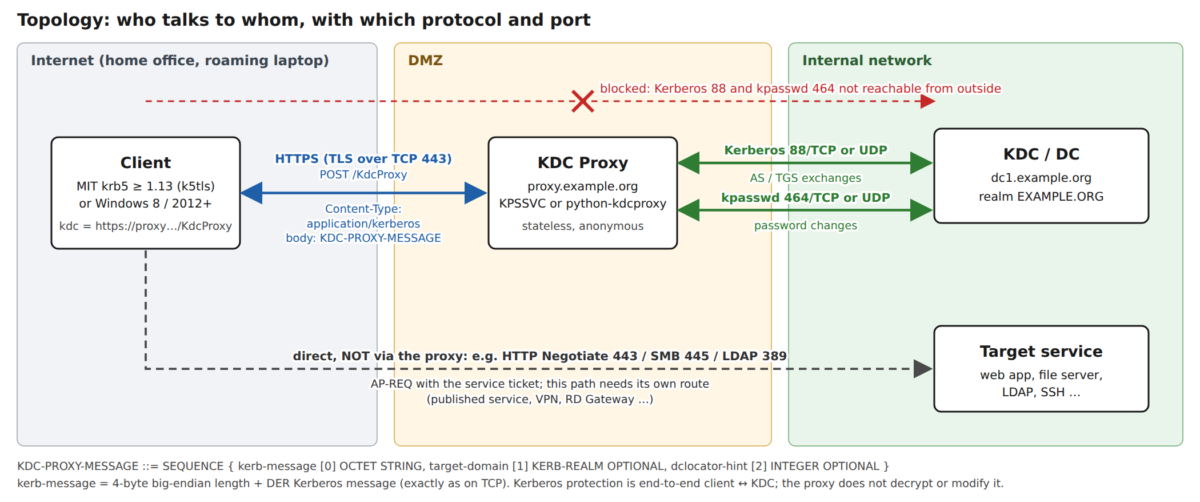
Kerberos over HTTPS: what a KDC proxy (MS-KKDCP) is for and how it works

Clients outside the internal network usually cannot reach the KDCs on port 88, but HTTPS on 443 works. A KDC proxy (MS-KKDCP) carries Kerberos messages inside HTTPS. This post explains the exact protocol flow, the client and server configuration, and the pitfalls.

Categories
Linux Network

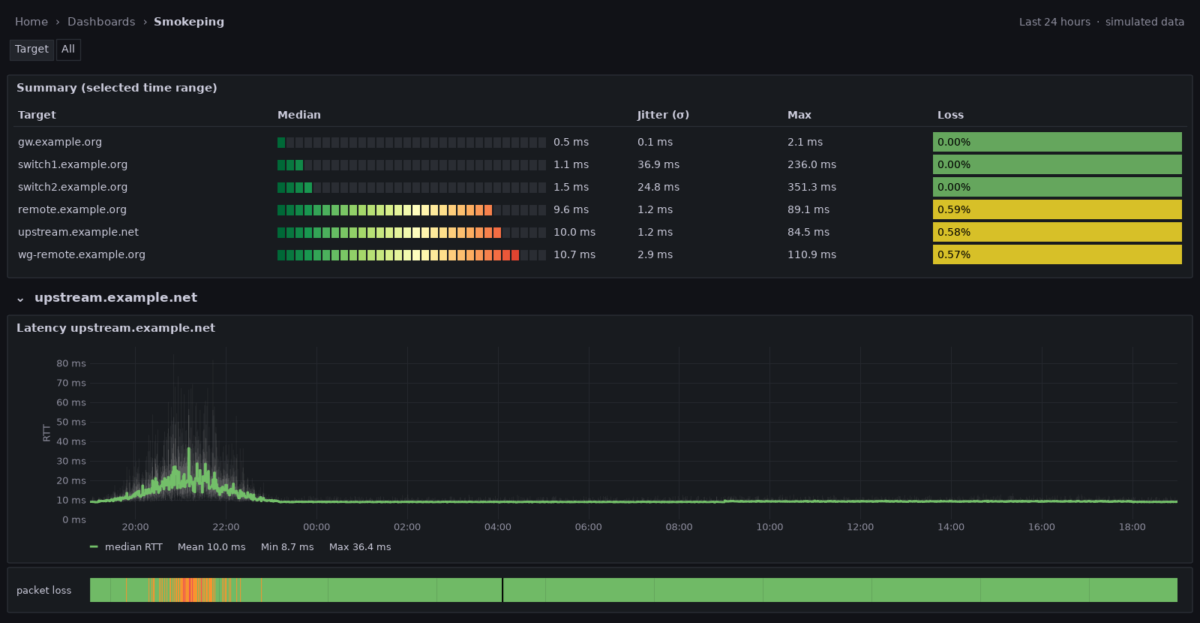
SmokePing without SmokePing: latency smoke graphs with Telegraf, InfluxDB and Grafana

SmokePing’s grey smoke shows at a glance whether a link is merely slow or unstable. If Telegraf, InfluxDB and Grafana already run, you don’t need SmokePing itself: Telegraf’s ping input sends the same 20-ping bursts and computes percentiles, and a few Grafana overrides draw the smoke. The probe, the dashboard, and two traps that cost me half of my samples.

Categories
Artificial Intelligence

Form or URL? The two elicitation modes in MCP

MCP servers can ask the user for input in the middle of a tool call. Form mode has the client draw a dialog; URL mode sends the user to a web page. How both work on 2025-11-25 and 2026-07-28, why secrets belong in URL mode, and what Open WebUI 0.13.2 does.

Categories
Artificial Intelligence

MCP Apps vs. regular MCP servers: what you gain and what you pay

MCP Apps let a server ship its own interactive UI into the chat. With a colour picker and a 3D viewer as examples: how it works, what you gain over plain tools and elicitation, and what it costs in confirmations, sandbox limits and host support.

Categories
Artificial Intelligence

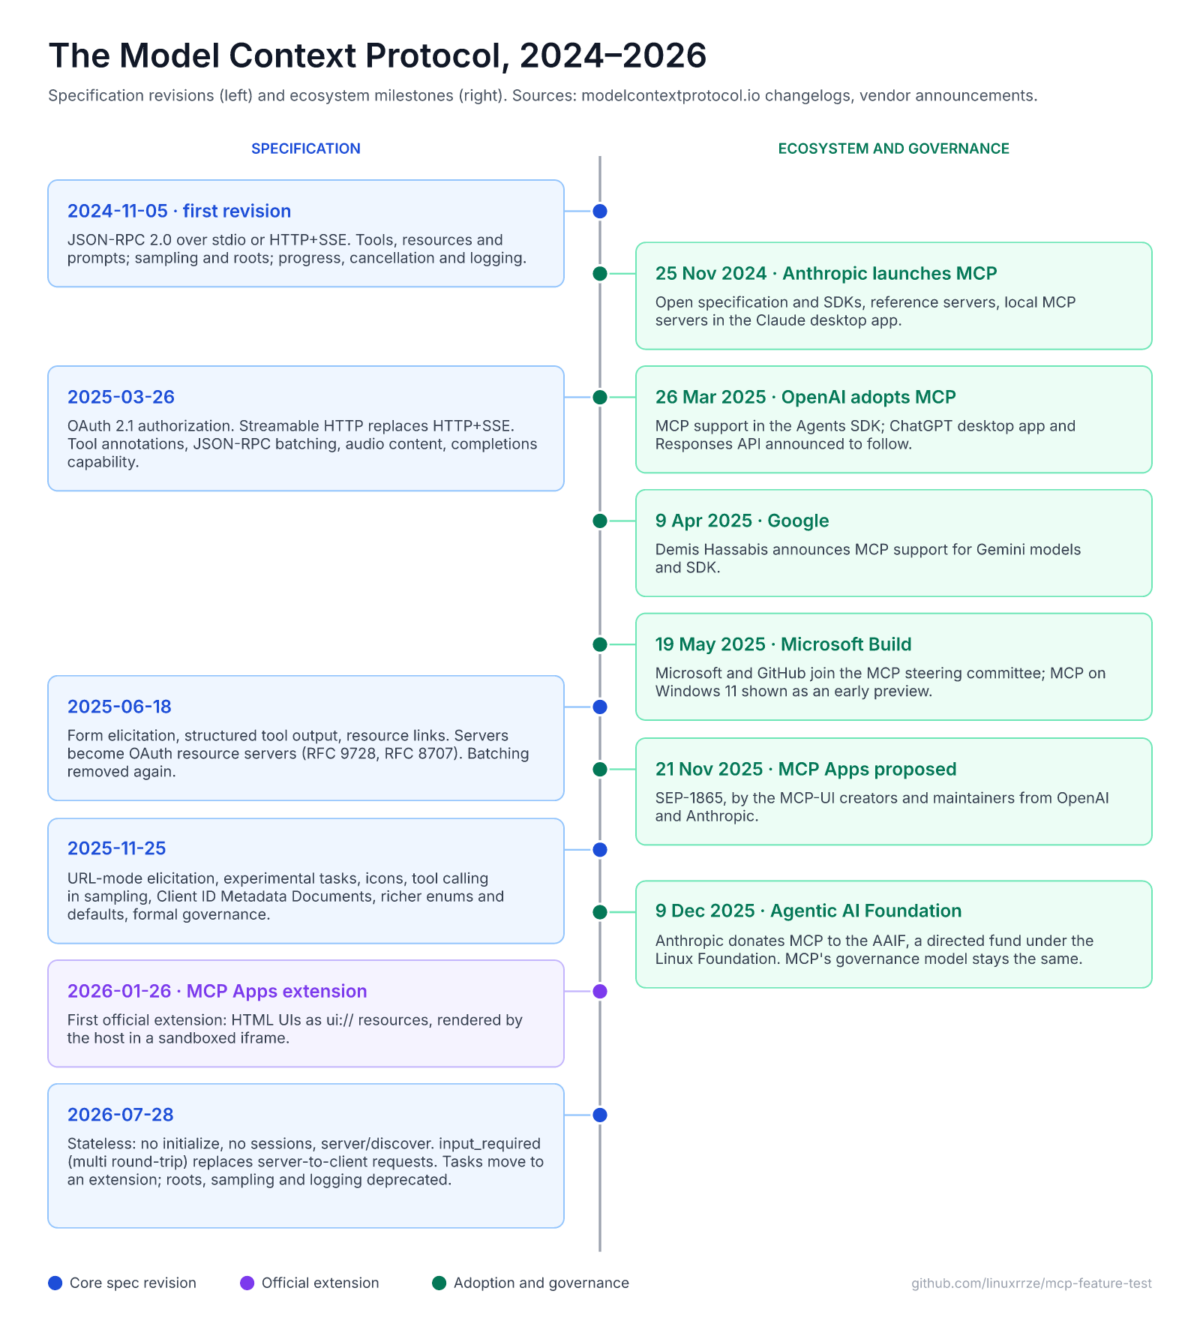
From stdio to stateless: a short history of the Model Context Protocol

Five specification revisions and one official extension in under two years: how MCP grew from a local tool protocol into a stateless, extensible standard under the Linux Foundation.

Categories
3D Printing Artificial Intelligence

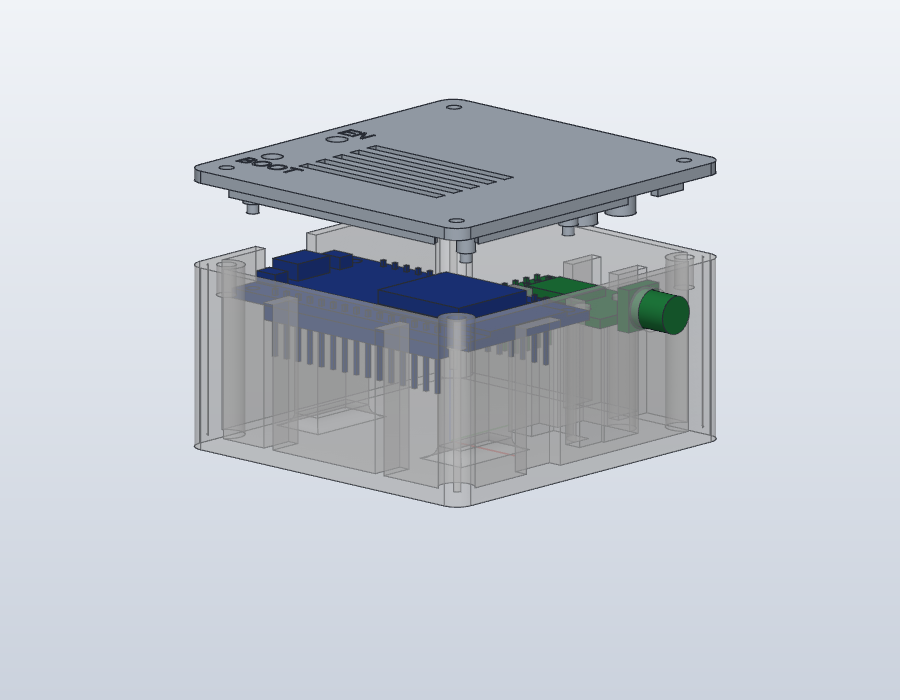
From one sentence to a printable case: an ESP32 + CC1101 enclosure designed with Claude Code

One sentence went in, a parametric 3D-printable enclosure for an ESP32 and a CC1101 radio came out: M2 heat-set inserts, a wiring-friendly layout, pegs that fit the boards’ real mounting holes, and a configuration table that adapts the whole box to a 30-pin or 38-pin ESP32. The final design, and a short summary of the fourteen versions it took to get there.

Categories
Linux Samba Windows

Samba AD, chrony and Windows 11: why signed NTP silently fails, and how to fix it

A Windows 11 domain member refuses to take its time from a Samba AD DC running chrony. Plain NTP works, the configuration is fine, yet the DC never answers. The cause: above functional level 2012, Windows uses the MS-SNTP extended authenticator, which neither chrony nor Samba support. I patched both, and after one more trap in the byte order, Windows now accepts the signed replies.