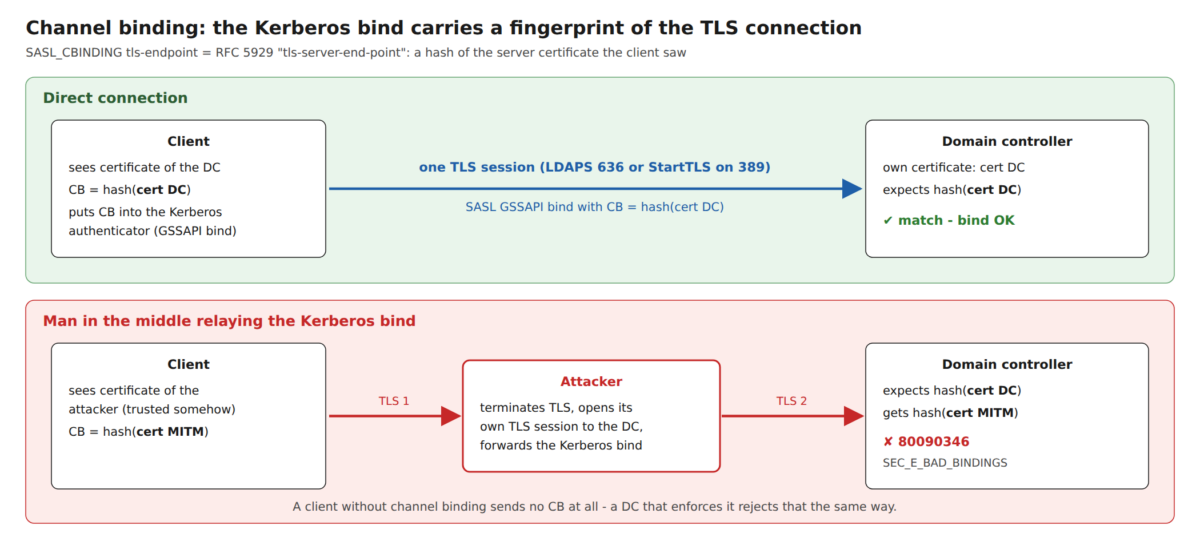
GSSAPI binds over LDAPS or StartTLS fail against hardened domain controllers with 80090346 or ‘Sign or Seal are not allowed if TLS is used’. Reproduced against a Samba AD DC with real output: what channel binding and the SASL security layer have to do with it, the two client settings that fix it, the matching server setting, and two traps when OpenLDAP itself accepts AD tickets.